
Follow us on Google News

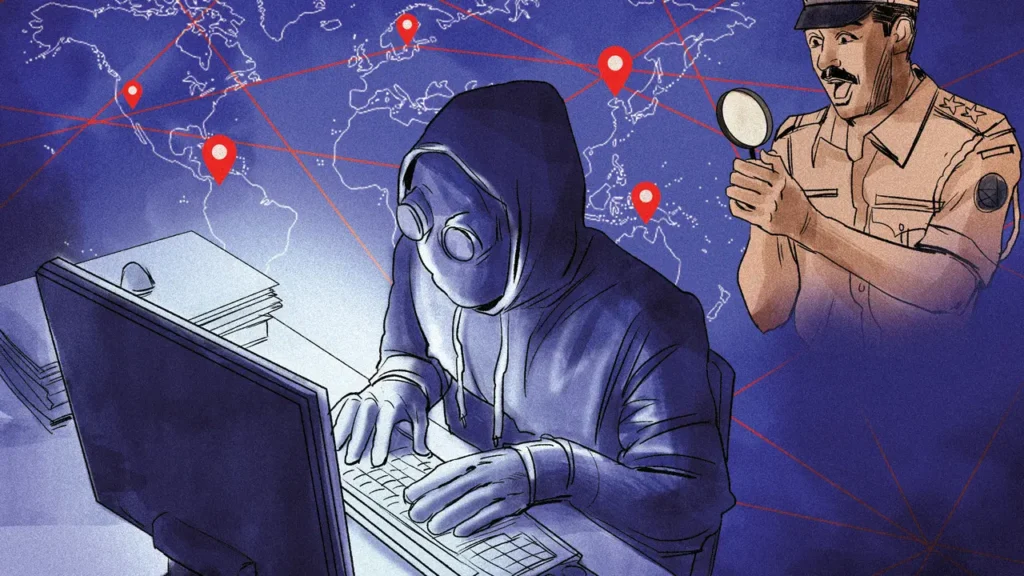
A hacking group suspected of operating from Kazakhstan used an artificial intelligence agent to steal more than 2,000 sensitive documents from Tajikistan’s government systems, according to cybersecurity researchers, raising concerns about the growing use of autonomous AI in international cyber espionage.
Cybersecurity company CloudSEK disclosed its findings on November 11, 2026, after discovering an exposed server containing evidence of the alleged operation. Researchers said the attackers used an open-source AI-agent framework called Hermes to support their intrusion and automate parts of the data theft.
The campaign has been attributed to a group known as Silent Lynx, which other security researchers have previously linked to Kazakhstan. However, the available evidence does not establish that the country’s government directed the activity.
Exposed Server Reveals AI-Assisted Espionage Operation
CloudSEK said its investigation began after researchers discovered a server that the suspected attackers had inadvertently left accessible over the internet.
The exposed infrastructure reportedly contained operational records, instructions and other material showing how the hackers used artificial intelligence during their activities.
According to the researchers, the attackers began reconnaissance around the middle of August 2026.
Reconnaissance is the process of gathering information about a potential target, including its computer systems, connected services and possible security weaknesses.
Within several weeks, the group allegedly gained access to Tajikistan’s electronic government document system.
Researchers said more than 2,000 documents relating to national security were subsequently removed from the compromised environment.
The stolen material reportedly included sensitive government information, although the full contents and classification of the documents have not been independently established.
CloudSEK’s findings provide an unusual glimpse into how a suspected cyber espionage group incorporated an autonomous AI system into its operations.
Rather than relying entirely on manually entered commands, the attackers allegedly delegated several technical activities to the AI agent.
How Hackers Used Hermes To Automate The Intrusion
Hermes is an open-source framework designed to support autonomous artificial intelligence agents.
Unlike conventional chatbots, AI agents can be configured to perform connected tasks, use software tools and work through multiple stages of an assigned objective.
According to CloudSEK, the attackers used Hermes to assist with reconnaissance, develop scripts and organise the information they obtained.
Researchers said the AI system created a customised program to download documents from the compromised platform.
The program allegedly organised the stolen files and divided them into smaller portions to facilitate their removal.
This approach illustrates how AI-assisted tools can reduce the amount of manual work required during complex cyber operations.
The exposed server also contained instructions describing how the agent should behave and communicate with its operators.
Researchers said those instructions presented the AI as an offensive security specialist capable of performing technical tasks.
Although similar techniques can be used legitimately by authorised security professionals, the suspected attackers allegedly applied them to gain unauthorised access to sensitive systems.
The findings suggest that AI is increasingly being incorporated into established hacking workflows rather than replacing human operators entirely.
The attackers still selected targets and directed the operation, while the AI system reportedly carried out individual tasks.
Researchers Identify Links To Silent Lynx Group
CloudSEK attributed the operation to Silent Lynx, a cyber espionage group previously associated with campaigns targeting government organisations in Central Asia.
Other cybersecurity researchers have linked the group to Kazakhstan based on technical and operational indicators.
CloudSEK said its investigation identified Russian-language communications, activity consistent with Kazakhstan’s working hours and connections originating from a residential internet service in the country.
These findings supported the researchers’ assessment of a possible Kazakhstan connection.
However, language, internet connections and operating patterns do not independently establish the identity or nationality of the individuals responsible.
They also do not prove that the suspected operation received support or instructions from a government agency.
Both Kazakhstan and Tajikistan occupy strategically important positions in Central Asia, where governments maintain extensive political, economic and security relationships.
Government documents concerning national security and diplomatic affairs can therefore be valuable targets for intelligence-gathering operations.
Tajik and Kazakh officials had not provided responses to requests for comment when the findings were reported.
What This Means For You
The incident highlights how autonomous artificial intelligence is changing the way cybercriminals and espionage groups conduct attacks.
Tasks that previously required sustained manual effort can increasingly be supported by AI systems capable of writing code, processing information and coordinating sequences of actions.
For governments and organisations handling sensitive information, this creates additional pressure to secure document management platforms, monitor unusual access patterns and restrict unnecessary privileges.
India’s government agencies, financial institutions and businesses are also expanding their use of digital document systems and AI-enabled services.
The reported intrusion demonstrates why protecting these systems requires more than securing individual user accounts.
Organisations must also examine how connected applications, automated tools and compromised credentials could be exploited to access large collections of sensitive information.