

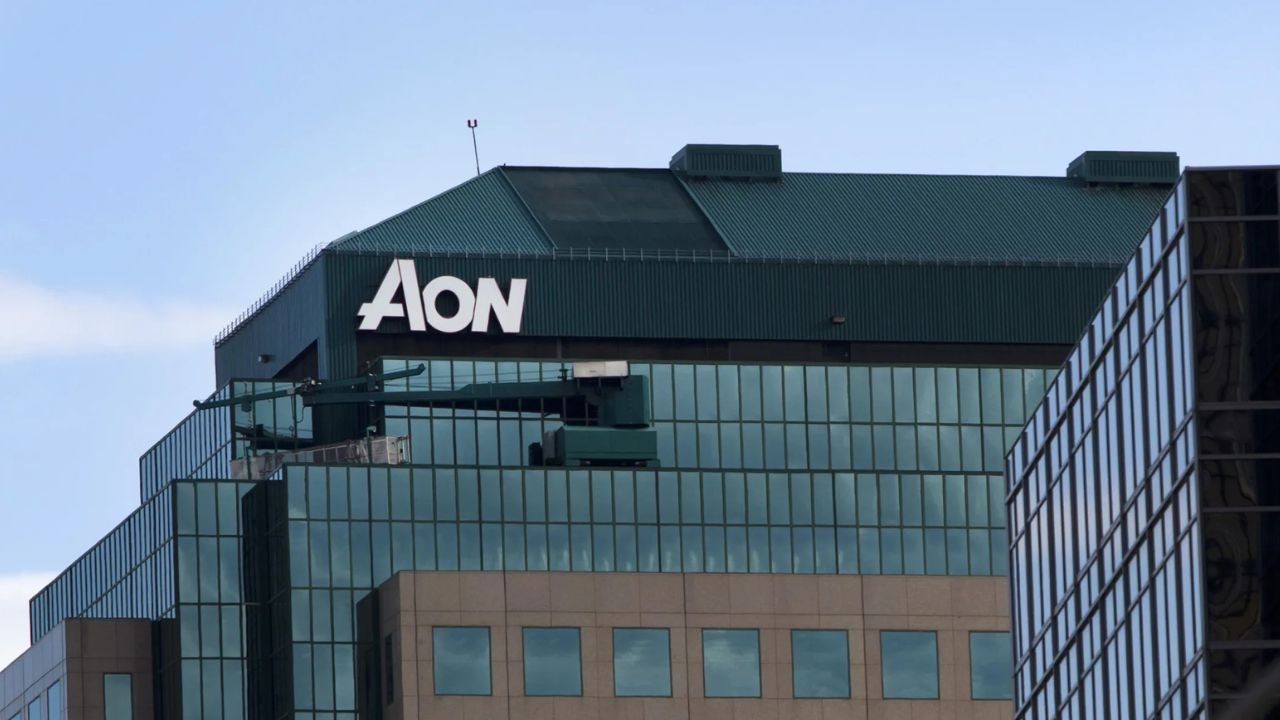
Aon plc, the global insurance, reinsurance and risk-management broker, has been listed on a data leak site operated by the Termite ransomware group, according to threat-monitoring service Kalir Pulse. The listing was detected at 01:07 UTC on October 7, 2026, but the claim remains unverified.
Aon has not confirmed a cyber incident, while no regulator filing or national CERT advisory cited in the available information has disclosed a breach involving the company. No proof-of-compromise sample, volume of allegedly stolen data or ransom deadline has been made public.
Kalir Pulse assigned the listing a high-severity assessment with a priority score of 55. However, it remains unclear which Aon entity, subsidiary or geographic operation the ransomware group is referring to.
FCRF Launches CP-FRM to Build India’s Next Generation of Fraud Risk Professionals
Aon Has Not Confirmed Any Breach
The leak-site listing is currently the only direct claim linking Termite to Aon. Aon has not issued a breach statement, and its recent cyber-risk publications dated September 22, October 1 and October 3 contain no reference to an incident affecting the company.
Key details that would normally establish the scale of a ransomware attack also remain unknown. There is no confirmed date of intrusion, no indication that Aon systems were encrypted and no evidence establishing whether the claim relates to Aon’s corporate network, a subsidiary or a third party.
There is also no confirmed information about the files allegedly obtained. No data volume, file count or specific categories of compromised information have been disclosed.
Given Aon’s business, potentially sensitive information held in its operations could include client risk assessments, underwriting submissions, policy and claims records, financial information and HR or employee-benefits data. These categories reflect the company’s areas of business and should not be treated as evidence that Termite obtained such information.
The listing follows several other recent claims attributed to Termite. Ransomware trackers recorded theLender and cable-management manufacturer Sealcon as alleged victims on September 22, while petroleum transporter Crossett was listed on September 26. The available tracker data indicates activity across unrelated sectors.
Leak Claim Could Carry Risks for Aon Clients
Any confirmed exposure involving a major insurance and risk-management broker could have implications beyond the company itself because brokers handle information supplied by corporate and public-sector clients.
Aon has previously warned clients about the consequences of third-party incidents. In a September 2026 advisory in South Africa, Jenny Jooste, Principal Broker for Cyber Solutions at Aon South Africa, said that a third-party incident does not necessarily mean a third-party liability.
Organisations whose information is compromised through a service provider may still face their own notification and compliance obligations, including requirements under legislation such as South Africa’s Protection of Personal Information Act.
Information held by insurance brokers could also be attractive to extortion groups because underwriting records may contain details about clients’ cyber insurance arrangements, security controls and incident-preparedness measures.
Aon’s October 2026 briefing on professional-services risks noted that cyber insurance underwriting increasingly examines security controls, governance and incident preparedness. If similar information were exposed in any breach, it could potentially provide attackers with insight into the security arrangements of affected organisations.
No evidence currently establishes that Termite has obtained such records from Aon.
There are also inconsistencies in publicly available descriptions of Termite itself. One tracker describes the group as first identified in late 2024 while also saying it has listed victims since May 2023. The same source gives differing figures for the group’s total number of victims.
Available reports generally associate Termite with modified Babuk ransomware code and a double-extortion model in which attackers steal information before encrypting systems. The group’s best-known previous claim involved Blue Yonder in November 2024, an incident that disrupted some downstream customers, including Starbucks.
How Termite May Operate Remains Separate From Aon Claim
There is no confirmed information about how Termite may have gained access to Aon, assuming the leak-site claim proves genuine. No available source describes an initial access method, dwell time or tools used against the company.
Reporting on other Termite activity has pointed to social-engineering techniques and stolen credentials as possible access routes.
A September 21 report by Ctrl Alt Nod linked some Termite intrusions to ClickFix campaigns, in which victims are persuaded to paste and execute commands through the Windows Run interface. According to that report, the campaigns delivered malware including LummaStealer and AsyncRAT and targeted organisations in sectors including healthcare, education and federal contracting. The report contains conflicting publication dates, leaving uncertainty around its timeline.
Separately, QPulse, citing a ParanoidLab exposure report, said passwords connected to Crossett had circulated before that company appeared on a ransomware leak site. The report linked some of the credentials to the Cavalier stealer family. Those findings relate to Crossett and do not provide evidence about Aon.
Aon has itself highlighted the growing use of impersonation and remote-access abuse by extortion groups. Its October 1 analysis of Luna Moth, also known as Silent Ransom Group, examined attackers who rely on social engineering rather than traditional software exploitation. That assessment concerned a different threat actor and does not establish the method behind the Termite claim.
Until Aon, a regulator or another primary incident source confirms the alleged compromise, the October 7 leak-site listing remains an unverified ransomware claim. The extent of any intrusion, the presence of stolen data and the potential impact on Aon or its clients have not been established.
Follow for daily updates on cybercrime, corporate fraud, DFIR, hacking, investigations, and digital forensics
