
Follow us on Google News

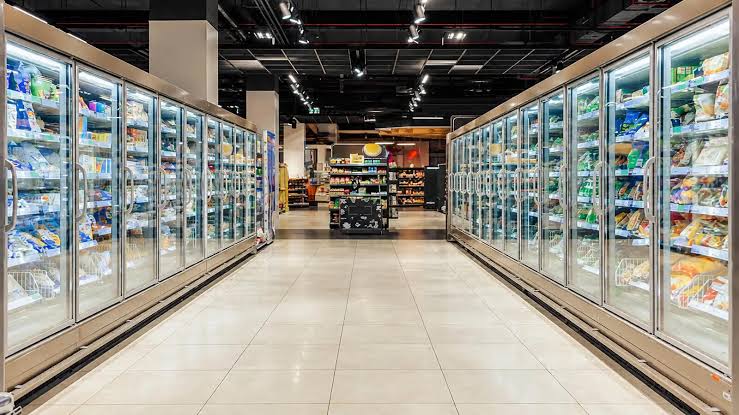
A confidential cybersecurity operation in the United Kingdom has helped prevent a potential cyberattack targeting refrigeration systems used by supermarkets, warehouses and other facilities. The intervention followed the discovery of vulnerabilities that could have allowed attackers to remotely interfere with refrigerators and freezers across multiple locations.
The operation was coordinated by the UK government and the National Cyber Security Centre (NCSC), amid growing concerns over cyberattacks affecting supermarket refrigeration systems in Europe.
How Was the Cyberattack Threat Discovered?
The security weaknesses were identified by Neil McCourt, an employee of refrigeration consultancy Omega Solutions, in equipment manufactured by Resource Data Management (RDM).
The vulnerabilities affected devices used to manage refrigeration systems in commercial environments. Researchers found that attackers could potentially exploit these weaknesses to gain control of vulnerable equipment and interfere with refrigeration operations across several sites.
Omega Solutions subsequently engaged cybersecurity consultancy Pen Test Partners to investigate the findings. Both organisations raised their concerns with RDM, recognising the potential consequences for supermarkets and the wider food supply chain.
FCRF Launches Certified Chief Risk Officer (CRO) Program for India’s Risk Leaders
Security specialists warned that exploitation of the vulnerabilities could have resulted in serious operational disruption, particularly where refrigeration equipment was controlled across multiple locations.
Why Were Supermarket Refrigerators Vulnerable?
The identified weaknesses involved RDM data managers, which are used to control refrigeration systems. Researchers warned that malicious actors gaining access to these devices could potentially manipulate refrigeration operations at different commercial premises.
The implications extended beyond individual supermarket stores because similar equipment was deployed across the food supply chain. Pen Test Partners also found that some exposed controllers could be identified relatively easily, while many others remained accessible online.
The researchers did not publicly disclose the method used to exploit the vulnerabilities, allowing affected organisations additional time to secure their equipment.
How Did the UK Government Respond?
After the vulnerabilities were confirmed, security researchers worked with government authorities to coordinate a response without publicly exposing the weaknesses before protective measures could be implemented.
Ken Munro, managing partner at Pen Test Partners, was attending a retail industry cybersecurity event when the findings emerged. This enabled him to meet NCSC representatives and share the intelligence directly.
The discovery prompted briefing calls involving retailers and officials from the NCSC, the Department for Environment, Food and Rural Affairs, and the Food Standards Agency. Pen Test Partners also attempted to contact owners of exposed refrigeration controllers so that affected organisations could take protective action.
The response focused on notifying vulnerable operators and preventing exploitation before attackers could use the weaknesses to disrupt refrigeration systems.
Why Did the Threat Raise Concerns Across Europe?
The discovery followed a series of cyberattacks affecting supermarket chains in at least seven European countries.
In October, hundreds of retailers across France experienced attacks described as being of unprecedented scale. French authorities publicly blamed Iran for those incidents.
Separately, the Pentagon was investigating a suspected cyberattack following refrigeration malfunctions at at least six American military bases in August.
The UK vulnerabilities were particularly concerning because researchers believed their exploitation could have produced disruption comparable to incidents that had already caused millions of euros in damage across continental Europe.
However, the reported UK operation concerned a potential attack that was prevented, rather than a confirmed successful compromise of the affected British refrigeration systems.
What Did the Manufacturer Say About the Security Flaws?
RDM chief executive Ged Evans said the vulnerability had been identified in a test environment and that the company’s testing procedures usually involved dismantling its hardware.
He maintained that the manufacturer had responded promptly to the issue and had already deployed its first software patches. The company had also contacted customers to identify potential problems and recommend measures to reduce their exposure.
The NCSC confirmed that it had shared security information and advice to help organisations understand the risks and implement appropriate protections.
Are Other Refrigeration Systems Still at Risk?
Although the coordinated operation helped protect many retailers, cybersecurity researchers warned that additional vulnerable systems could remain exposed.
Pen Test Partners indicated that some controllers were straightforward to locate, while others were more difficult to identify. The firm withheld technical details of the vulnerability to reduce the likelihood of further exploitation.
The incident highlights how cyber vulnerabilities in equipment used for everyday commercial operations can threaten essential services beyond conventional computer networks.
For supermarkets, warehouses and food distribution businesses, interference with refrigeration systems could create operational and financial consequences even without attackers directly accessing payment systems or customer databases.
The UK intervention demonstrated the importance of cooperation between security researchers, manufacturers, retailers and government agencies in addressing weaknesses before they are exploited.