Follow us on Google News

Ukrainian police, working in coordination with the United States Federal Bureau of Investigation, have arrested four suspected members of an international ransomware syndicate accused of extorting roughly Rs 378 crore from at least 28 companies worldwide. A two-year investigation revealed that the group targeted critical infrastructure alongside businesses in the oil and gas, pharmaceutical, manufacturing, logistics, and financial sectors.
According to the National Police of Ukraine, the criminal organization comprised at least 27 individuals with links to Ukraine, Kazakhstan, Russia, and other countries. Investigators identified the group as part of a larger transnational cybercrime network exceeding 60 members operating across eight jurisdictions, with ties to former members of the Conti ransomware group. Authorities have not officially confirmed whether the four arrested suspects were former Conti operatives or members of the BlackSuit and Chaos ransomware gangs.
Corporate Targets and Extortion Demands
Before launching attacks, syndicate members thoroughly researched target companies’ financial standing, assets, staff, and IT vulnerabilities. Once inside corporate networks, hackers exfiltrated sensitive business data and encrypted system files, demanding millions of dollars in cryptocurrency for decryption keys while threatening to leak stolen records publicly.
Acting head of Ukraine’s National Police, Maksym Tsutskiridze, stated that at least 28 victim companies have been identified so far, paying more than $40.5 million, or approximately Rs 378 crore, in ransom. He noted that this figure represents only confirmed payments and that total damages remain under assessment. Court documents list Warren Oil Company, Maxis International-USA, Newpark Resources, and Quantum Health as potential victims. Records indicate Warren Oil Company was breached in August 2024, losing 1.4 terabytes of data and paying 84.5 Bitcoin, valued at roughly Rs 46.72 crore at the time. Newpark Resources allegedly paid around Rs 14 crore in December 2024, while Quantum Health paid roughly Rs 46.72 crore in June 2026 following an initial demand of $15 million, or about Rs 140 crore.
Use of AI Voice Tools to Deceive Employees
The syndicate integrated artificial intelligence into its social engineering operations. Attackers posed as internal IT support personnel by phone, utilizing a specialized platform capable of generating AI-powered voice messages. Under the pretext of offering technical assistance, hackers persuaded employees to surrender login credentials or install remote access software on their workstations.
In several instances, one operative kept an employee occupied on the phone while another simultaneously breached the company network. Investigators uncovered fake corporate VPN login pages, spoofed phone numbers, and remote administration tools such as TeamViewer and AnyDesk. In the Warren Oil Company breach, an employee was tricked into entering credentials on a counterfeit login portal, enabling attackers to capture two-factor authentication codes, infiltrate the network, steal sensitive data, and encrypt files.
Coordinated Raids Across 66 Locations
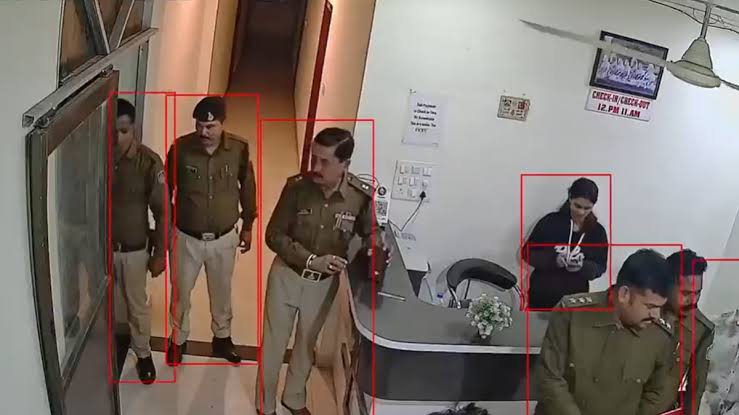
Under the joint operation, law enforcement officers conducted simultaneous searches across 66 locations in Kyiv and 11 other regions of Ukraine, resulting in the detention of four key suspects. Police seized computers, mobile phones, bank cards, roughly $370,000, or approximately Rs 3.45 crore, in cash, and 20,000 euros, valued at about Rs 20.5 lakh.
The four detainees have been formally notified of charges relating to participation in a criminal organization and unauthorized interference with information systems. They remain in custody and face up to 15 years in prison under Ukrainian law if convicted. Investigators continue working to identify remaining network members and additional corporate victims, having released footage of the raids, seizures, and interrogations, including an audio recording of an alleged ransom call demanding $15 million.