
Follow us on Google News

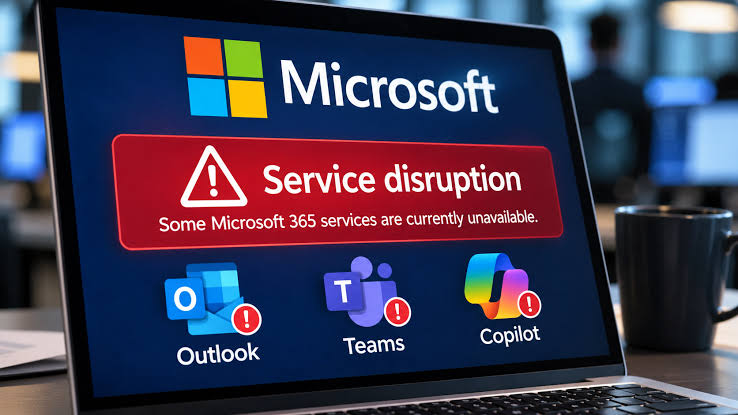
New Delhi: A global outage affecting Microsoft 365 services in November 2026 disrupted government operations, official emails, and enterprise functions across 74 countries and territories, while India’s central government email system remained operational. The uninterrupted functioning of official Indian communication resulted from a policy framework established years earlier that mandated a dedicated system managed by the National Informatics Centre (NIC) instead of relying on global commercial platforms. The incident has now highlighted the need for India to extend this sovereign digital architecture across its broader administrative systems, critical infrastructure, and public services.
The global disruption began on November 12 and continued into the next day, preventing government departments and institutions worldwide from accessing emails, sharing documents, and using enterprise tools. Microsoft attributed the failure to servers becoming unexpectedly unavailable and stated that there were no indications of malicious cyber activity, though a final root cause analysis remains pending. Across several nations, the operational fallout was immediate. Officials in Japanese ministries could not send emails for nearly an entire workday and had to revert to paper copies of documents. In the United Kingdom, email communications at NHS England were affected, some police forces were unable to receive online crime complaints, and the Bank of England confirmed disruptions while maintaining critical operations. In Singapore, the government technology agency reported issues in certain systems, even as emergency services and Singpass continued functioning.
Similar disruptions were recorded in Australia, where multiple government departments including the intelligence agency ASIO faced service interruptions. In the United States, the House of Representatives experienced email disruptions, and several municipal governments advised residents to contact offices by telephone instead of online channels. In contrast, no public reports emerged in India by November 13 indicating failures in core payment systems, major government digital platforms, or essential public services. While experts caution against viewing this as proof of complete immunity across the entire digital ecosystem, the episode underscores how India’s official communication network avoided the global breakdown.
Policy Framework Behind India’s Email Resilience
The foundation for India’s separate email infrastructure dates back to the government’s first email policy formulated in 2014 and later amended in October 2024. Under this policy, NIC holds central responsibility for managing government email services, and designated government organizations are required to use the NIC platform, barring specific exemptions. Following a tender issued in 2023, the government upgraded the service to a cloud-based platform, selecting Zoho Corporation as the master system integrator within NIC’s institutional framework. Under this arrangement, ownership and control of government data remain strictly with the state. According to a written reply presented in the Lok Sabha on April 1, 2026, nearly 16.68 lakh official email accounts had been migrated to the upgraded platform.
This structure ensured that India did not merely substitute one foreign vendor with another, but retained institutional accountability and technical control within its own architecture. Consequently, when Microsoft Exchange Online experienced an outage, the NIC network remained unaffected, mirroring its resilience during the July 2024 CrowdStrike global tech disruption. A parallel institutional separation exists within India’s financial sector, where banking and payment networks operate on dedicated national platforms under regulatory supervision, distinct from the productivity and email software used by bank staff. During the July 2024 disruption, the Reserve Bank of India noted only minor impacts on 10 banks and non-banking financial companies, as most core banking systems were not hosted on external cloud setups. Similarly, no systemic failure in core banking or payment infrastructure was publicly confirmed during the November 2026 outage, though formal assessments from the RBI and the National Payments Corporation of India are awaited.
Shifting Focus From Cybersecurity to Cyber Resilience
The global outage demonstrates that organizations with strong security defenses can still face operational paralysis if an external technology provider fails. While cybersecurity focuses on preventing intrusions and attacks, cyber resilience ensures that essential services continue operating during technical failures or attacks and recover rapidly. Analysts note that India should not evaluate its cyber posture solely through international rankings or single-vendor telemetry, such as Microsoft’s Digital Defense Report, which attributed 2.5 percent of observed customer threat impacts between January and June 2026 to India. Such vendor-specific data cannot measure a nation’s overall ability to maintain essential services during systemic disruptions.
India’s institutional response capacity has expanded considerably in recent years. In 2025, the Indian Computer Emergency Response Team (CERT-In) handled 29,44,248 cybersecurity incidents, issuing 1,530 alerts, 390 vulnerability notes, and 65 advisories in coordination with NCIIPC, the RBI, sectoral regulators, critical infrastructure operators, and law enforcement agencies. However, maintaining continuity during large-scale technical outages requires moving beyond incident response to structural independence.
Six Measures to Strengthen Digital Infrastructure
To build long-term resilience, six key measures have been identified for India’s digital ecosystem. First, authorities including CERT-In, NCIIPC, and relevant ministries must conduct a national assessment of the outage’s actual impact across government, banking, healthcare, telecom, transport, and critical infrastructure. Second, critical institutions should be required to map their dependencies across cloud services, email, identity management, DNS, and software supply chains. Third, institutions must demonstrate through regular emergency drills that essential operations can continue for 24, 48, and 72 hours without major technology providers.
Fourth, the government needs to accelerate the development of certified Indian cybersecurity products, research laboratories, and indigenous technologies. Fifth, the institutional model of the NIC email policy should be extended to identity management, document management, e-Office, and other core government applications. Sixth, regulators such as the RBI, SEBI, and NCIIPC must evaluate concentration risks arising from over-reliance on specific foreign or domestic platforms. Additionally, India’s own email system requires continuous testing of data portability, alternative access, disaster recovery, and backups to ensure that reducing dependence on global vendors does not create a new single point of failure with a private domestic integrator.