

State Bank of India is investigating suspected exposure of personal information linked to 3,897 customers on the dark web.
What Did SBI Discover?
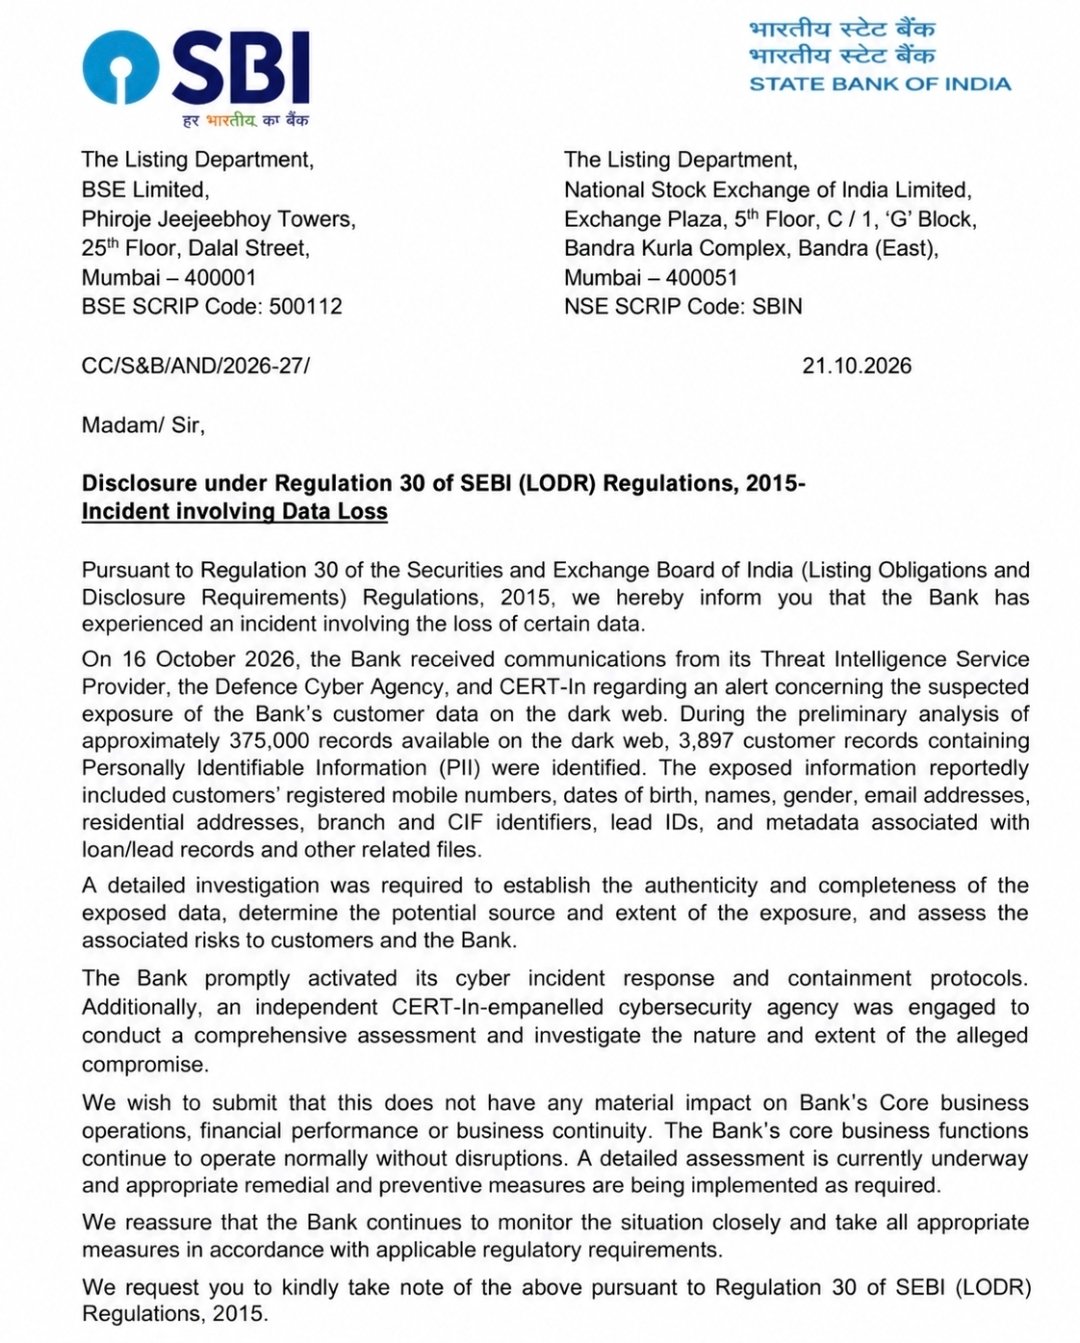
State Bank of India (SBI) has disclosed a suspected exposure of customer information after a preliminary examination of approximately 3,75,000 records available on the dark web identified 3,897 records containing personally identifiable information (PII).
In a regulatory filing dated October 21, 2026, the bank said it received alerts on October 16 from its threat intelligence service provider, the Defence Cyber Agency and the Indian Computer Emergency Response Team (CERT-In). These communications concerned the suspected exposure of customer information on the dark web.
The bank said a detailed investigation was necessary to verify the authenticity and completeness of the information, determine its possible source and establish the extent of the suspected exposure. The assessment will also examine potential risks to customers and the institution.
FCRF’s Chief AI Officer Certification Returns on November 14 to Prepare Future AI Leaders
What Customer Information Was Exposed?
According to SBI’s disclosure, the records reportedly contained customers’ registered mobile numbers, dates of birth, names, gender, email addresses and residential addresses. The information also included branch identifiers, Customer Information File (CIF) identifiers, lead IDs and metadata associated with loan and lead records.
These details could raise privacy and security concerns if confirmed as authentic. However, the bank has not established the full circumstances surrounding the suspected exposure, including how the records became accessible or whether all the information identified during the preliminary analysis is genuine.
The investigation is expected to clarify these questions and assess the possible implications for affected customers.
What Steps Has SBI Taken?
SBI said it promptly activated its cyber incident response and containment protocols after receiving the alerts. It also engaged an independent cybersecurity agency empanelled by CERT-In to conduct a comprehensive assessment of the suspected compromise.
The agency will investigate the nature and extent of the incident, while the bank continues implementing appropriate remedial and preventive measures. SBI said it was closely monitoring the situation and taking necessary steps in accordance with applicable regulatory requirements.
Has the Incident Affected Banking Operations?
SBI maintained that the suspected data exposure has not materially affected its core business operations, financial performance or business continuity. It confirmed that essential banking functions were continuing normally without disruption.
However, the detailed investigation remains underway. The bank has not yet established the authenticity, source or complete extent of the suspected exposure.
The420 Insight: The incident underlines the importance of protecting customer information and promptly investigating suspected data leaks. Customers should remain cautious about unsolicited calls, messages or emails requesting banking details, particularly when personal information may have been exposed.
Follow for daily updates on cybercrime, corporate fraud, DFIR, hacking, investigations, and digital forensics
