

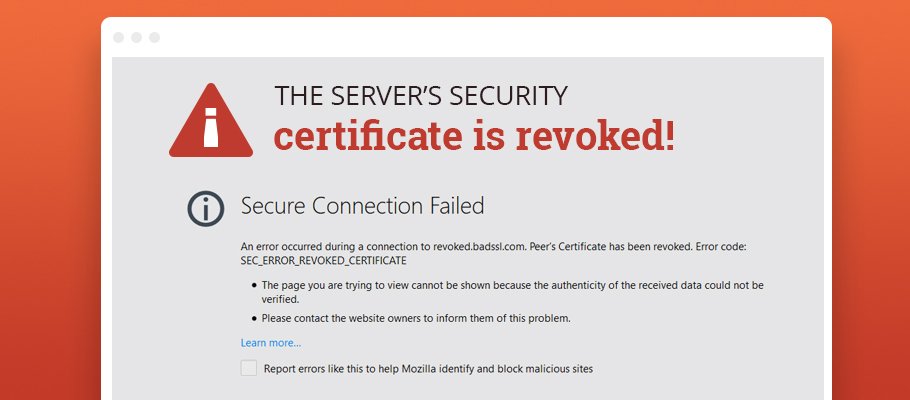

A nineteen-year-old hacker who previously uncovered vulnerabilities in the Central Board of Secondary Education’s online marking system has flagged major security concerns across several Indian government websites. Nisarga Adhikary claimed that multiple public portals continue to operate using revoked and expired digital security certificates issued by eMudhra. He stated that several web browsers have already started refusing to load these pages, warning users that the connections are unsafe. The revelations point to an ongoing administrative lapse across central departments following a major security scare involving the certification provider.
Flaws in eMudhra keys prompt global security scare
The root of the issue lies in cryptographic certificates previously issued by eMudhra. An examination revealed that a set of private keys generated by the agency suffered from insufficient randomness. This structural weakness made the underlying keys easier to recover, triggering widespread international security alarms.
Security analysts noted that such flaws could allow unauthorized actors to produce fraudulent transport layer security certificates. Under these conditions, malicious operators could impersonate official government platforms or execute man-in-the-middle attacks to intercept user traffic. Although the alert was sounded globally, the continued presence of invalid certificates on official portals has raised questions about timely remediation by the concerned departments.
Complaint lists critical services across central ministries
Following his findings, Adhikary submitted a formal complaint on October 24, 2026, naming ten government websites and digital services that continue to run revoked certificates. The complaint highlights platforms managed by several key central ministries, including services overseen by the Ministry of Electronics and Information Technology.
Among the affected portals identified in the complaint are language translation platform Bhashini, Software Technology Parks of India, and the Information Security Education and Awareness initiative. Key public services managed by other ministries were also named, including portals for the Ministry of Railways, the Census of India, and the National Crime Records Bureau under the Ministry of Home Affairs. The list further includes the National Scholarship Portal under the Ministry of Education, the Digital Life Certificate for Pensioners managed by the Department of Personnel and Training, the Telecom Regulatory Authority of India, and the Nuclear Fuel Complex under the Department of Atomic Energy.
Centre orders investigation as provider exits business
The continued deployment of invalidated certificates has raised alarms regarding citizen data protection, as these portals handle sensitive records, law enforcement data, and public welfare distributions. Browser warnings citing revoked certificates directly affect public access to key administrative services, prompting concerns over trust and digital infrastructure safety.
In response to the broader controversy, the union government ordered a formal inquiry into the lapses surrounding the eMudhra certificates. Following the regulatory scrutiny and the emergence of cryptographic vulnerabilities, eMudhra announced its decision to exit the website security certificate business altogether. However, Adhikary stated that the persistence of revoked certificates on active government domains demonstrates that vital infrastructure has yet to complete the required security transitions.
Follow for daily updates on cybercrime, corporate fraud, DFIR, hacking, investigations, and digital forensics
