Follow us on Google News

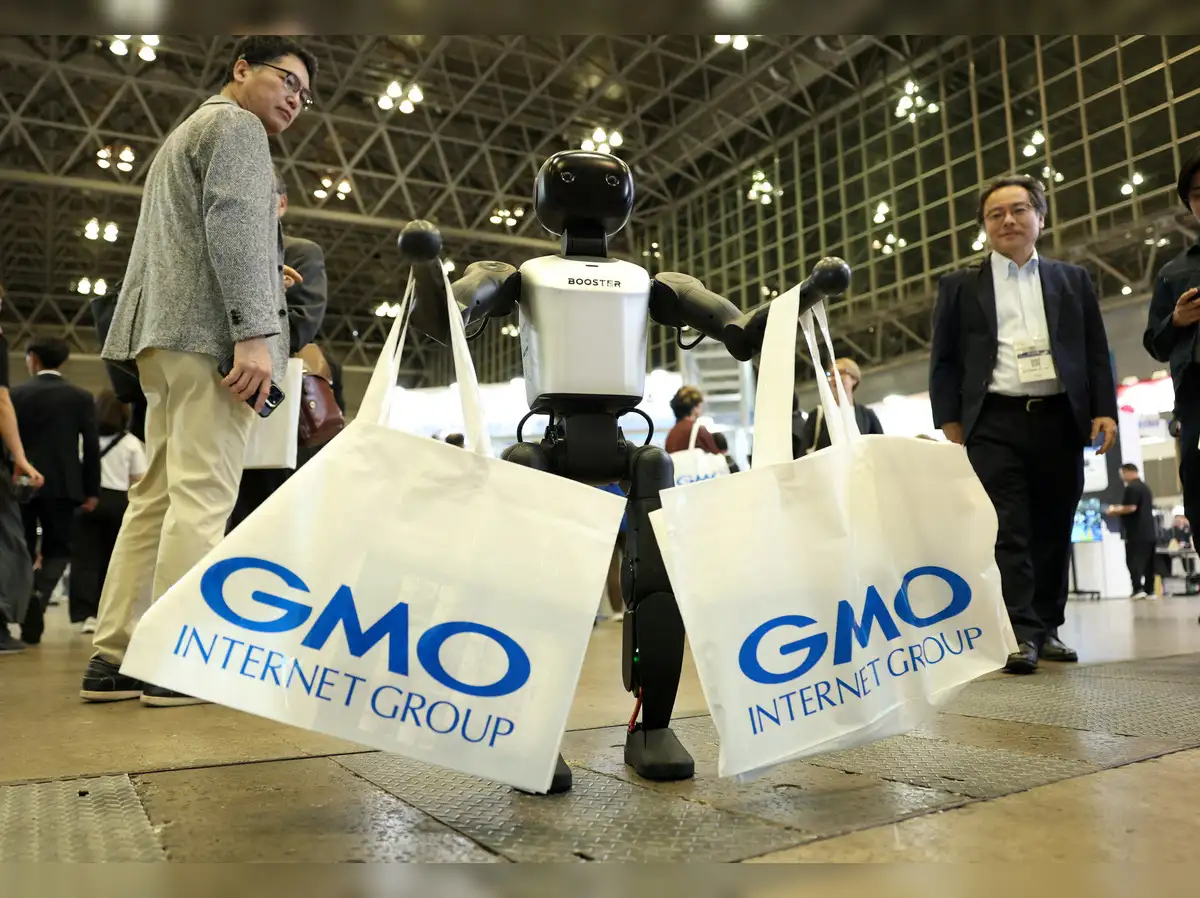
Japan’s GMO Internet Group has apologised after a cyberattack compromised its cloud service, exposed customer information and enabled unauthorised transactions in financial accounts. The company’s chief executive has acknowledged that security weaknesses identified internally in 2024 were not addressed adequately before the breach.
CEO Masatoshi Kumagai made the admission at the company’s first public press conference since the incident emerged last month. He said experts from GMO Cybersecurity by Ierae, a subsidiary specialising in cybersecurity, had flagged system-related problems in April 2024.
The parent company failed to take sufficient action on those warnings, Kumagai acknowledged. He said the organisation’s response had not been thorough or fast enough and apologised to customers and other affected parties.
The incident involved Onamae.com Desktop Cloud, a service that provides remote Windows desktop environments. Attackers gained unauthorised access, stole information and enabled transactions that customers said they had not initiated.
Security Warnings Raised Two Years Before The Attack
The admission has raised questions about how GMO handled security concerns identified within its own group.
According to the company’s explanation, specialists at GMO Cybersecurity by Ierae had reported vulnerabilities in the system in April 2024. However, the parent company did not take sufficient measures to address the concerns.
Kumagai acknowledged that the warnings were not properly escalated to him. The company also said it had prioritised maintaining stable services without conducting adequate analysis of which security measures needed urgent attention.
The failure is significant because the warning came from a specialist cybersecurity subsidiary within the same corporate group. It suggests that identifying a technical weakness is not enough if the organisation responsible for fixing it does not act on the information.
GMO subsequently carried out emergency maintenance operations, but those measures did not prevent the intrusion. The company began investigating the incident on October 19 after receiving customer inquiries and confirmed the installation of malicious software in some customer environments the following day.
It shut down the affected cloud service on October 21 to prevent further damage.
More Than 26,000 Cases And Unauthorised Financial Transactions
The breach affected GMO’s Onamae.com Desktop Cloud service, which customers used to access remote computers, including environments for foreign exchange and securities trading.
Information was taken from the compromised systems, while some customers reported transactions in their trading accounts that they had not authorised. The incident affected dozens of securities firms and other businesses.
At its November 2 briefing, GMO reported more than 26,000 cases connected with the incident. Earlier reporting put the number of potentially affected servers at approximately 26,739.
The company has promised to compensate customers for confirmed realised losses resulting from unauthorised trading. It has also offered a flat payment of 5,000 yen to every customer using the affected service, regardless of whether they suffered a direct financial loss.
GMO has refused to pay the attackers’ ransom demand. The company has also announced a $1 million reward for information that helps identify and secure the arrest of those responsible. It said it had received more than 400 submissions through its cybercrime bounty programme.
The company has acknowledged that attackers deployed ransomware, although it has not publicly established every detail of the malware’s impact. It is working with law enforcement and other organisations as the investigation continues.
Executives Face Pay Cuts As Company Promises Security Overhaul
The public apology was accompanied by financial penalties for senior management. Kumagai will take a 30% reduction in pay for three months, while other senior executives will also accept salary cuts of between 20% and 30%.
Kumagai also apologised for social media posts, including a photograph in which he appeared to be smiling, which he acknowledged could have hurt the feelings of affected customers.
GMO has promised to replace its security system and overhaul its approach to protecting customer information and financial assets. It has also committed to working with external specialists and relevant authorities to investigate the breach and prevent similar incidents.
The financial impact remains uncertain. Beyond compensation payments, the company faces the cost of rebuilding systems, investigating the intrusion and restoring customer confidence.
The case has also drawn attention to Japan’s wider cybersecurity preparedness. Companies increasingly depend on cloud platforms and remote access systems to support financial services and business operations, making weaknesses in one service capable of affecting customers across several organisations.
The incident demonstrates that cybersecurity failures can extend beyond the systems directly operated by a company. When customers store access credentials or conduct financial activity through a compromised service, the consequences can reach their accounts and assets.
What this means for you:
If you use remote desktop or cloud services to access financial accounts, avoid storing trading credentials in environments that have not been independently secured. Enable multi-factor authentication, review account activity regularly and contact your broker immediately if you notice transactions you did not authorise.