
Follow us on Google News

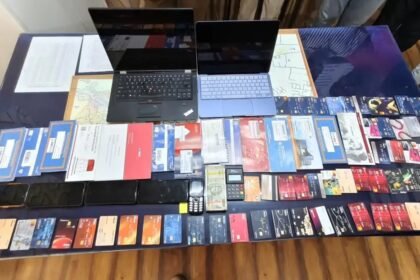
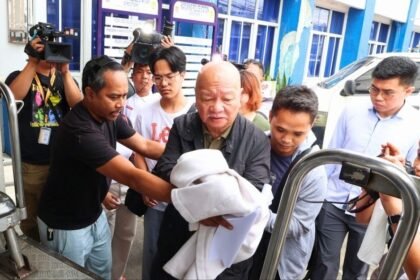
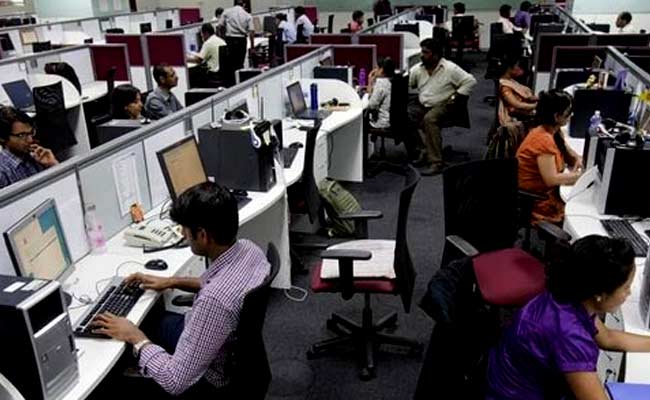
EW DELHI: A cross-border cyber fraud syndicate linked to an illegal call centre in Hyderabad’s Madhapur area targeted nearly 20 lakh American citizens, siphoning off an estimated $27.39 million, or approximately Rs 261 crore, across a span of 14 months, according to findings by the Enforcement Directorate. The central financial probe agency arrested four additional suspects on Wednesday following an investigation that exposed a transnational conspiracy spanning India, the United States, Dubai, and Hong Kong. The scam systematically targeted elderly Americans, many born in the 1940s, through deceptive pop-up notifications, fabricated virus alerts, and fraudulent purchase messages. The operational footprint of the network initially detected in Hyderabad subsequently led enforcement sleuths to illegal call centre hubs situated in Chandigarh, Patiala, and Pune.
Deceptive Operations and Role Specialisation
The syndicate operated through a structured corporate hierarchy where call centre personnel were categorised into distinct functional units to execute the deception. Initial operators, designated as diallers, made contact with targeted individuals using automated systems hosted on overseas servers in Germany and Finland. Once contact was established, operators termed bankers assessed the financial profile, bank balances, and asset holdings of the victims. The calls were then transferred to senior operatives known as closers, who posed as federal agents representing the Drug Enforcement Administration, Department of Justice, Federal Trade Commission, and US Treasury. To fabricate legitimacy, callers displayed forged identification cards, official badges, fraudulent seizure notices, and bogus court decrees. Victims were informed that their bank accounts were implicated in drug trafficking or money laundering probes, and were coerced into surrendering their life savings under the guise of safe government custody.
Doorstep Couriers and Gold Collections
The fraudulent scheme moved beyond digital manipulation to direct, physical extortion across American soil. Operatives deployed local associates within the United States to collect cash and bullion directly from the residences of elderly victims. Under instructions from call centre handlers, frightened targets purchased physical gold bars, packaged cash inside parcel couriers, completed wire transfers, purchased gift cards, or deposited money through Bitcoin automated teller machines. Investigators identified an arrested suspect, Jaswant Singh, as the key coordinator overseeing cash pickups and parcel receipts on the ground in the United States. In addition, the agency recovered compromised Social Security numbers belonging to 140 Americans, which were utilised by the syndicate to establish front commercial entities and receive shipments under assumed names, thereby obscuring the identities of the actual perpetrators.
Money Laundering and Overseas Infrastructure
The siphoned proceeds were funnelled through a layered laundering conduit involving US mule bank accounts, dummy commercial firms in Dubai and Hong Kong, cryptocurrency transfers, and traditional hawala networks before arriving in India. WhatsApp groups analysed by investigators recorded 927 approved transactions totalling $27.39 million between July 2025 and September 2026. Cryptocurrency functioned as a dual mechanism for the network, serving as a medium to transfer stolen capital and as a payment vehicle using the dollar-pegged stablecoin USDT to purchase stolen databases, virtual dialling services, and offshore server bandwidth. According to the agency, illicit gains repatriated to India were channelled into real estate acquisitions, bullion, luxury automobiles, and commercial ventures, with the Hyderabad zonal unit continuing its asset recovery proceedings.