Follow us on Google News

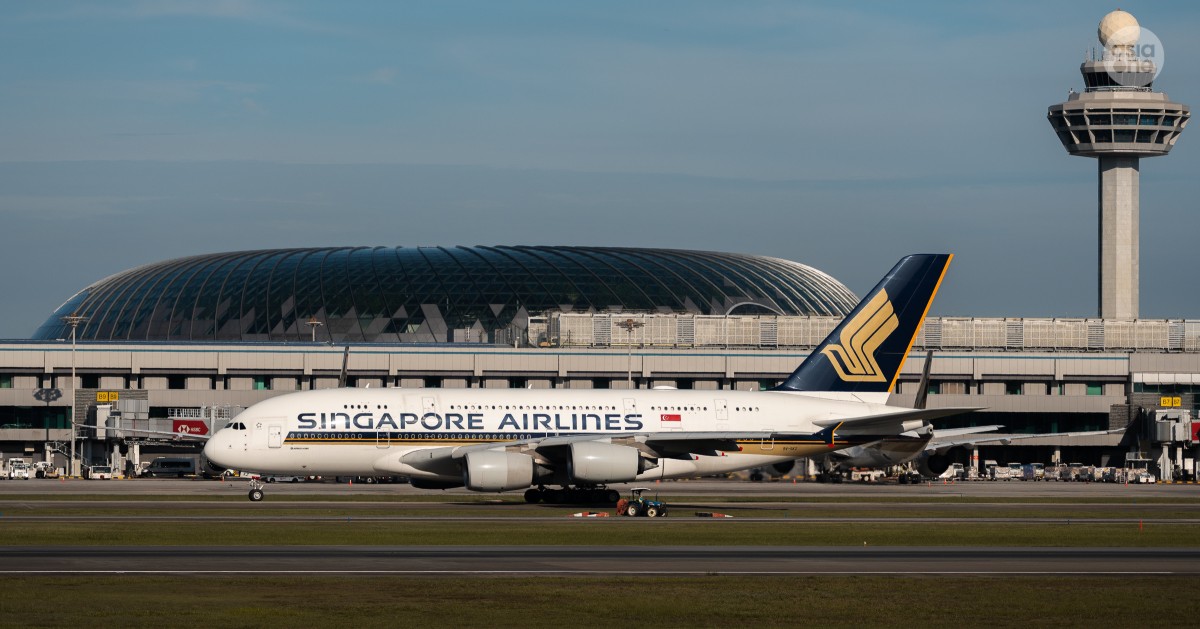
Singapore Airlines has disclosed that approximately 46,000 booking records may have been affected by a cybersecurity incident involving Amadeus, its reservation technology provider.
The airline confirmed that its internal IT systems were not breached, but passenger information stored within the external booking environment may have been exposed. The incident has also affected several other international airlines.
What Passenger Information Was Exposed?
The potentially compromised information includes customer names, booking reference numbers, travel itineraries and booking classes.
Singapore Airlines said additional personal information may have been accessed in approximately 620 booking records. This included email addresses, telephone numbers, travel document details and KrisFlyer membership numbers. The airline has not indicated that every affected booking contained all these categories of information.
Were Banking and Payment Details Compromised?
Amadeus confirmed that customers’ bank account information and credit card details had not been leaked during the incident. The company also stated that existing reservations had not been modified.
https://the420.in/fcrf-certified-chief-ai-officer-second-cohort-november-2026/
Singapore Airlines emphasised that its own IT infrastructure remained unaffected, with the cybersecurity incident involving systems operated by its external technology provider.
What Action Is Singapore Airlines Taking?
The airline has begun contacting affected passengers who have upcoming travel plans. As a precautionary measure, Singapore Airlines said it would change booking reference numbers associated with affected reservations.
The measure is intended to address concerns arising from the possible exposure of booking information. There was no indication that passengers’ travel arrangements had been altered as a result of the incident.
How Did the Amadeus Breach Occur?
Amadeus said it had identified a vulnerability affecting an environment used to display travel bookings. The weakness potentially exposed information associated with reservations processed through its systems.
However, the company did not provide an overall figure for the number of customers affected across airlines using its services. The incident has drawn attention to cybersecurity risks associated with shared reservation technology.
Which Other Airlines Were Affected?
Several international carriers, including Cathay Pacific, Japan Airlines, Malaysia Airlines and South Korea’s Asiana Airlines, have reported customer data concerns connected to the Amadeus incident.
Cathay Pacific disclosed that information relating to approximately 53,000 bookings was affected. Japan Airlines separately reported that the incident involved data belonging to around 92,000 customers.
These figures cover different categories of affected records and individuals and are not directly comparable. The incident highlights how vulnerabilities in third-party technology systems can expose customer information across multiple airlines without requiring attackers to breach each carrier’s internal network.